
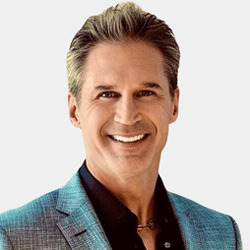
Chuck Davis
Vice President, Global Information Security
Hikvision


Chuck Davis is Vice President of Global Information Security at Hikvision, where he leads international cybersecurity strategy, governance, product security, and cyber resilience initiatives. With more than 25 years of experience spanning IBM, The Hershey Company, and Hikvision, he believes effective cybersecurity starts with understanding both the technology and the business, then applying that understanding to manage risk, build resilience, and enable innovation. Chuck is also the founder of NetBOM and writes about cybersecurity and artificial intelligence on his blog, Between the Hacks.
Fun fact: I am a named inventor on ten patents, and I’ve spoken about cybersecurity in more than 20 countries.
Learn more about the Denver CISO community here.
Give us a brief overview of the path that led to your current role.
I didn’t set out to build a career in cybersecurity because, when I started, the field was still emerging. My career began at PSINet, one of the pioneers of the commercial Internet, where investigating someone who was using our mail server to relay spam sparked a lifelong fascination with information security. That curiosity led me through leadership roles at IBM, The Hershey Company, and back to IBM before joining Hikvision.
Looking back, I’ve realized my career has never really been about security technology for its own sake. It’s been about understanding risk, solving complex problems, and helping organizations adopt new technologies securely and confidently.
What is one of your guiding leadership principles?
Stay curious.
Technology changes too quickly for any leader to have all the answers. I’ve found that the best decisions come from asking thoughtful questions, listening to diverse perspectives, and being willing to challenge your own assumptions. Curiosity drives continuous learning, but it also keeps us from becoming too comfortable with yesterday’s answers to tomorrow’s problems.
What is the greatest challenge CISOs face today, and how are you addressing it?
The greatest challenge CISOs face today is the speed at which technology, threats, and the risks they create are evolving. AI is accelerating that change, while cloud transformation, geopolitical tensions, and an increasingly complex technology ecosystem continue to reshape the attack surface.
Addressing that requires more than governance or compliance. Compliance establishes an important baseline, but compliance does not equal security. I focus on understanding where the greatest risks actually are, building strong technical and organizational security capabilities, and creating the resilience to respond effectively when incidents occur. At the same time, cybersecurity has to enable the business to adopt new technologies and innovate without taking unnecessary risk.
We won’t predict every threat or prevent every incident. The goal is to build a security program that anticipates emerging risks, adapts quickly to the unexpected, and continues protecting the business as the environment changes.
What is the key to success for someone just starting out as a CISO?
Learn the business before trying to change it.
Cybersecurity leaders are most effective when they understand how their organization creates value, what it depends on, and what keeps their executive peers awake at night. Technical expertise gives you credibility, but understanding the business and building trusted relationships are what allow you to influence decisions.
How do you measure success as a leader?
I measure success by what happens when I’m not in the room.
If my team is making good decisions, challenging assumptions, collaborating effectively, developing future leaders, and continuously improving without depending on me for every answer, then I’ve done my job. Great leaders don’t create followers. They create other leaders.
What is the value of being a member of Gartner C-level Communities?
One of the greatest benefits of Gartner C-Level Communities is the opportunity to learn from peers who face similar leadership challenges in very different industries.
Cybersecurity can become insular if we only look to our own profession for answers. Some of the best ideas I’ve implemented didn’t originate in cybersecurity. They came from conversations with leaders in healthcare, manufacturing, finance, retail, and government. Those different perspectives challenge assumptions, spark new ideas, and make us better leaders.
Governing Body members share their insights and leadership perspectives to shape the agendas and topics that address the top priorities impacting business leaders today.
By CISOs, For CISOs®
Find your local community and explore the benefits of becoming a member.