Boston CISO Community
Executive Summit
December 3, 2026 | Renaissance Boston Seaport District
December 3, 2026
Renaissance Boston Seaport District
Join fellow CISOs for a day of peer connections, peer perspectives and Gartner insights
The Gartner Boston CISO Community Executive Summit is the community’s signature event, bringing together CISOs for a full day of immersive, peer-driven discussions and curated networking. Connect with peers who share similar priorities, exchange real-world experiences and gain data-driven insights from Gartner analysts. Walk away with practical solutions, validated strategies and valuable connections, giving you greater confidence to lead through change.
Participate in discussions on the most critical issues impacting CISOs today:
Scaling AI and Digital Transformation Through Proactive Governance and Risk Management
Integrating Cyber Resilience into Core Business Strategy and Operational Excellence
Leveraging Security Insights to Unlock Growth, Efficiency, and Market Differentiation


Boston CISO Governing Body
The Governing Body Co-Chairs shape the summit agenda, ensuring that all content is driven By CISOs, For CISOs®.
Governing Body Co-Chairs
Javed Ikbal
Bright Horizons
VP/CISO
Jasvinder Khera
John Hancock
CISO

Brian McGowan
SharkNinja
CISO

Ravi Thatavarthy
Primo Brands
CISO
What to Expect at an Executive Summit

Gain New Perspectives from Peers
Hear from CISO practitioners and thought leaders on how they're solving critical challenges impacting your role in Keynote sessions, and participate in smaller, interactive discussions with your peers in Breakout and Boardroom sessions.

Strengthen Your Peer Network
Catch up with familiar faces and build new relationships in your Boston CISO Community through dedicated networking time in an intimate environment and curated, one-on-one conversations with peers matched based on shared priorities and interests.

Leverage Gartner Insights
Gain data-driven insights and field-tested best practices from a Gartner analyst in the opening Keynote, setting the context for peer conversations throughout the day on the most critical topics affecting your role.
Agenda
8:00am - 8:30am Registration & Breakfast
8:30am - 9:15am Gartner Keynote
How AI Changes the Operating Model
Miles Gibson, Ph.D.
VP Analyst
Gartner
Accelerating changes to IT operating models. As technology becomes easier to build and deploy, creativity and problem solving become core competencies, and IT shifts focus from delivery efficiency to ongoing innovation. Organizations seeing the greatest impact are redefining ownership, breaking down functional silos, and creating new ways of working that bring business, technology, and risk leaders together around shared outcomes.
Join this keynote to explore:
- How AI is merging accountability for business, technology, and risk outcomes
- Why cross-functional teams are becoming the default model for delivering value at speed
- How trust is becoming a competitive advantage in a technology-driven enterprise
9:15am - 9:40am Networking Break
9:40am - 10:25am Breakout Session
From Noise to Proof — Reinventing Vulnerability Management
Hosted by Horizon3.ai
Eric von der Linden
Senior Technical Director, Americas
Horizon3.ai
Most security programs measure effort — not outcomes. CISOs patch thousands of vulnerabilities and deploy countless tools, yet real resilience depends on proving defenses actually work. Organizations are shifting from assumptions to evidence using autonomous pentesting to view environments through an attacker’s lens.
Join this session to come away with insights on:
- Prioritizing real attack paths and exploitable vulnerabilities
- Closing the find, fix, verify loop with measurable improvement
- Reducing attacker dwell time with offense informed detection
9:40am - 10:25am Breakout Session
The Future of Out-of-Band Solutions
Ryan Klaer
CISO
Insulet

Jinks Shirgaonkar
Director, IT Security, Risk and Compliance
ICU Medical
Maintaining visibility and control during a cyber incident is becoming a critical leadership priority. Out-of-Band solutions provide independent access and management capabilities that help organizations respond to disruptions, recover faster, and reduce operational risk. Explore how emerging OOB technologies are shaping the future of cyber resilience and business continuity.
Join this session to learn how to:
- Leverage Out-of-Band capabilities to maintain visibility and control during cyber incidents
- Advance business continuity strategies to reduce operational risk and improve organizational resilience
- Build a more resilient operating model that supports continuity during outages and attacks
9:40am - 10:25am Executive Boardroom
Privilege, Integrity, Recovery — The New Rules of Enterprise Data Protection
Hosted by Cohesity

James Blake
Vice President of Global Cyber Resiliency Strategy, Response & Consulting Services
Cohesity
Yves Dorleans
CISO
Keolis North America
As AI accelerates the creation and utilization of data, organizations face unprecedented challenges in securing their most valuable asset. Shadow AI, dark data, and the proliferation of distributed applications have rendered traditional data protection methods insufficient. In this evolving threat landscape, security leaders must adopt risk-based, adaptive strategies to safeguard innovation, ensure compliance, and maintain operational resilience.
Join this boardroom session to discuss:
- Unifying data protection and compliance across workloads
- Ensuring regulatory compliance and business continuity through robust, future-ready solutions
- Accelerating cyber recovery with AI-driven tools
9:40am - 10:25am Executive Boardroom
The AI Governance Blueprint — Redefining Endpoint Strategy
Hosted by GLOW-US-DE
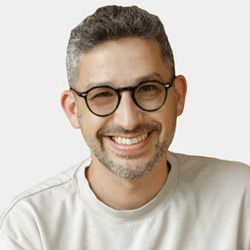
Arnon Joseph
Chief Product Officer
Glow
Building an endpoint strategy for the AI era is critical to closing visibility gaps and strengthening prevention where work gets done. This boardroom will explore how shifting from reactive incident response to proactive endpoint security provides the essential foundation needed for a strong AI governance policy.
Join this boardroom to discuss:
- Why the endpoint is the necessary foundation for robust AI governance
- Where traditional EDR leaves visibility gaps
- Practical ways to reduce risk before data exposure occurs
10:25am - 11:10am Networking Break
10:35am - 11:00am Peer-to-Peer Meetings
Peer-to-Peer Meetings
Connect with like-minded peers in a one-on-one setting through Peer-to-Peer Meetings. You will be matched with peers in your community based on your shared interests and priorities.
11:10am - 11:55am Breakout Session
Staying Ahead of AI Data Risks
Hosted by Concentric AI
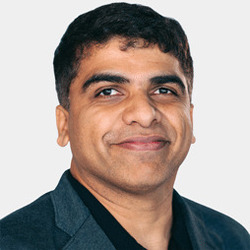
Madhu Shashanka
Cofounder, Chief Scientist and Co-CTO
Concentric AI
AI is quickly becoming one of the biggest drivers of enterprise productivity—and one of the fastest-growing sources of data security risk. As copilots, assistants, and public AI tools become embedded in daily workflows, sensitive data flows into systems that most security teams can't fully see, understand, or control. To stay ahead, organizations must rethink their security strategies and harness AI’s potential to protect what matters most.
Join this session to discover:
Why AI is a rapidly growing, unseen enterprise risk
Where legacy data security falls short with AI
How to enable AI innovation without added data exposure
11:10am - 11:55am Breakout Session
Breakout session
Hosted by Censys
Details coming soon.
11:10am - 11:55am Executive Boardroom
Rethinking Security for the Age of Agents
Hosted by Cyera

Jeremiah Salamon
Information Security Officer
Choate, Hall & Stewart

Richard Walzer
CISO
Clean Harbors
Agents are becoming the biggest opportunity in the enterprise, and the biggest adversary. They read your data and act under borrowed identities, at a speed no human review process was built to match. The old question in security was how to keep bad actors out. The new one is more complex: how do you create and manage the biggest risk in your own enterprise, the agents you deployed on purpose?
Join this boardroom to discuss:
- Establishing a framework where data, identity, and agent security operate as one system
- Shifting from asking whether you can trust your agents to determining what access they can be trusted with
- Balancing innovation and risk by creating visibility needed to understand agent activity
11:10am - 11:55am Executive Boardroom
Recovery as a Compensating Control — Defending the Undefendable
Hosted by Veeam

Simon Le Comte
VP, Systems Engineering
Veeam
Jasvinder Khera
CISO
John Hancock

Michael Nichols
CISO
CIRCOR International
When legacy systems can’t be patched, recovery becomes a key compensating control. CISOs rely on recovery documentation as evidence to protect themselves and their organizations. This session covers how immutable backups and traceable recovery records withstand regulatory and legal scrutiny after incidents and how forensic and threat intelligence data can turn reactive recovery into a documented, risk-based decision.
Join this session to learn:
- How recovery and immutable backups protect unpatched legacy systems
- Building recovery records for regulatory and legal review
- Using forensic and threat intelligence to justify response decisions
11:55am - 12:30pm Lunch Service



Apply to Participate
Each application is carefully vetted to ensure members meet established criteria, preserving the quality of the network and enabling meaningful, peer‑level discussions among leaders from the world’s leading organizations.
Once you submit your application, a Community Program Manager will schedule a conversation to understand your priorities and interests and complete onboarding, including access to year‑round community events.
Location
Venue & Accommodation
Renaissance Boston Seaport DistrictA block of rooms has been reserved at the Renaissance Boston Seaport District at a reduced conference rate. Reservations should be made online or by calling +1 617-338-4111. Please mention Gartner CISO Executive Summit to ensure the appropriate room rate.
Deadline to book using the discounted room rate of $229 USD (plus tax) is November 9, 2026.
Your Community Sponsors
Global Thought Leader

CISO Thought Leaders


Key Sponsors

Program Sponsors



Community Program Manager
For inquiries related to this community, please reach out to your dedicated contact.